How to Build AI Agent Payment Features in Fintech Apps
Create engaging, high-performance mobile applications tailored to your business needs. We craft future-ready apps that offer smooth user experiences on all devices.
Build robust and scalable websites and CMS platforms that help you manage content effortlessly. Our development ensures a seamless digital presence.
Launch secure, feature-rich online stores with intuitive shopping experiences. We build tailored eCommerce platforms designed for growth.
Design captivating games with immersive gameplay and stunning graphics. From concept to launch, we build engaging experiences that players love.
Enhance your customer relationships with customized Salesforce implementations. Drive growth and efficiency with smarter CRM solutions.
Harness artificial intelligence and machine learning to automate workflows and gain actionable insights. Our AI transforms data into smart decisions.
Accelerate your software delivery lifecycle with continuous integration, delivery, and infrastructure automation to boost efficiency.

TL;DR
Your payment stack was designed around one assumption: a human taps the button. AI agents break that assumption, and every control you built on top of it.
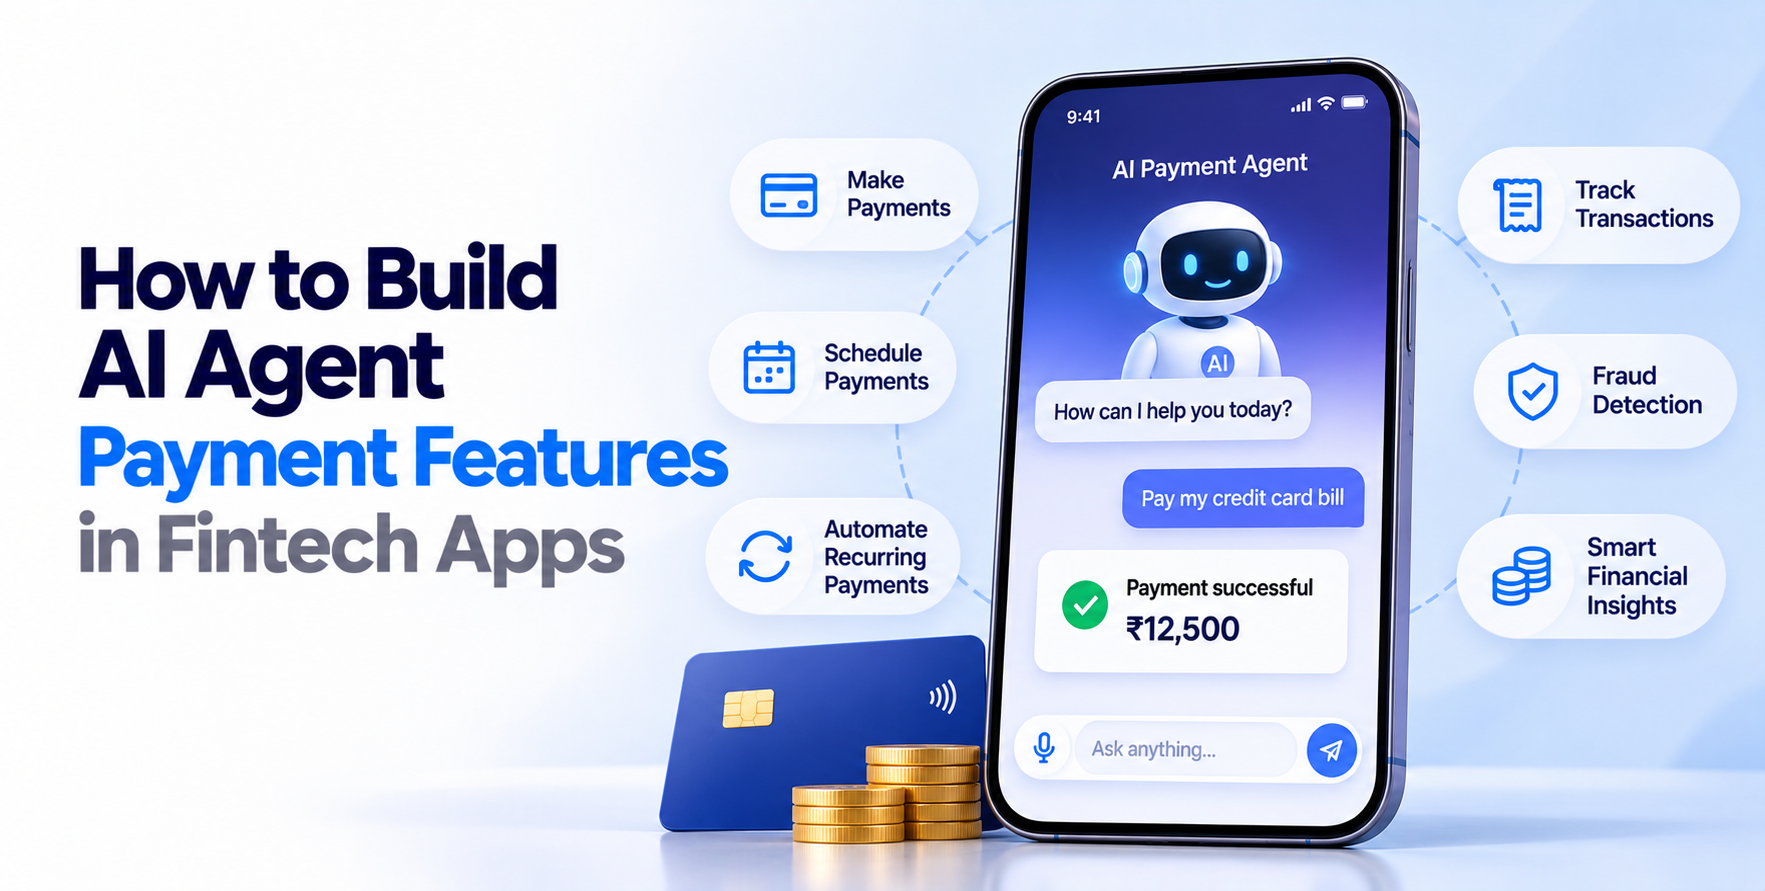
Learning how to build AI agent payment features means designing a system where software, not a person, initiates or completes a transaction within limits the user set in advance. The hard part is never the API call.
It is proving who the agent was, what it was authorized to do, and that it stayed inside those bounds. This guide walks through the architecture, the build order, and the controls that keep it defensible.
Juniper Research projects agentic commerce spend will reach $1.5 trillion globally by 2030, growing out of the pilot deployments running through 2025 and 2026.
Card networks are building for it already. Visa’s Trusted Agent Protocol and emerging Know Your Agent frameworks exist because merchants need a way to tell an authorized agent from a bot. If you are building fintech infrastructure now, agents are a design input, not a future feature.
Teams asking how to build AI agent payment features usually mean one of three different things. They need different architectures.
The agent prepares the payment and the user approves it. Lowest risk, fastest to ship, and the right starting point for most consumer apps. Authorization stays human, so your existing consent flows mostly survive.
The user grants standing permission with boundaries: a spend ceiling, an approved category, an expiry date. The agent transacts without asking each time. This is where most real value sits and where most of the engineering work lives.
A buyer-side agent negotiates with a seller-side agent, and settlement happens between them. Highest complexity, thinnest standards, and realistic today only in narrow B2B contexts.
Ship the first pattern, architect for the second, and watch the third.
Every agent needs a verifiable, revocable identity separate from the user’s credentials. That means a cryptographic key pair, a registration record, and a certificate the merchant or acquirer can validate.
Never let an agent reuse the user’s session token. Identity is what makes revocation possible, and revocation is what makes the feature safe to launch. Teams that already run API development with proper service authentication will recognize the pattern.
A mandate is the machine-readable contract between the user and the agent. It states the maximum per transaction, the maximum per period, the eligible merchants or categories, the expiry date, and the conditions requiring human approval.
Store it immutably, version it, and evaluate it server side on every attempt. A mandate checked only in the client is not a control, it is a suggestion.
The payment rail stays conventional. What changes is the gate in front of it. Before the charge goes out, the execution service validates the agent certificate, loads the active mandate, evaluates the transaction against every constraint, checks velocity, and only then calls the processor.
One idempotency key per agent intent prevents a retry loop from spending twice.
Log the agent identity, the mandate version, the decision inputs, the model or policy that triggered the action, the outcome, and the timestamp. Make it append-only. When a user disputes a charge their agent made, this log is the only thing standing between you and an automatic chargeback loss.
Before any code, write the schema a user mandate will take. Fields for spend ceiling, period, merchant allowlist, category restrictions, expiry, approval thresholds, and revocation status. Get legal and risk to review it as a document, because that is effectively what it is.
Everything downstream reads from this structure, so changing it later means migrating live authorizations. Teams that rush past this step end up hardcoding limits in business logic where nobody can audit them.
Build registration that mints a key pair per agent instance, binds it to a user account, and records it in a registry your execution service can query. Support immediate revocation and short certificate lifetimes.
Expose a user-facing screen listing every active agent, what it may spend, and a one-tap kill switch. Users will not trust agentic payments without a visible off button, and regulators increasingly expect one.
This is the core of how to build AI agent payment features defensibly. Create a single service every agent-initiated transaction must pass through. It loads the mandate, evaluates constraints in a fixed order, applies velocity checks, and returns allow, deny, or escalate.
Keep the logic declarative so a risk analyst can read it. Routing all agent traffic through one gate means you can tighten rules globally without redeploying agents.
Never hand an agent a raw card number or account credential. Provision a network token scoped to that agent and mandate, so compromise is contained and revocation is instant.
Your actual money movement reuses infrastructure you likely already have, whether that is card rails, ACH, or the same patterns used in payment app development. The agent layer sits above it and never replaces it.
Define the thresholds that force a human decision: a new merchant, an amount above a set percentage of the ceiling, an unusual time, a category not seen before. Build the approval into push notification and in-app flows with a short expiry.
Make declining frictionless. The escalation path is what lets you raise agent autonomy gradually, starting conservative and loosening limits as behavioral data accumulates.
Existing fraud tooling helps, but it was trained on human patterns. The best practices to prevent fraud in fintech apps still apply, though agent traffic needs its own behavioral baseline rather than inheriting human thresholds.
Agentic payments do not get a regulatory exemption. Strong customer authentication still applies, and the mandate grant is usually where the authenticated consent happens. Your records must show the user authorized that specific scope, at that time, with that method.
Dispute handling needs a position before launch: when an agent makes a purchase the user regrets, who absorbs it? Write the policy, surface it in the mandate flow, and keep evidence linked to each transaction.
Model governance enters scope too. If an LLM decides what to buy, you need its version, prompt, and inputs recorded against the payment. This overlaps heavily with the fintech compliance checklist work most teams already run, extended to cover autonomous actors.
The teams that get this right are not the ones with the cleverest agent. They are the ones whose mandate layer, identity model, and audit trail were designed before the first payment moved. That is the real answer to how to build AI agent payment features that survive a regulator, a dispute, and a bad model release.
EngineerBabu builds agentic payment infrastructure inside production fintech products, from mandate design through tokenization and audit. Start a conversation about your build.
Yes, when the user grants explicit, authenticated, scoped authorization in advance. The legal basis is the mandate, so its clarity and evidence trail determine whether the authorization holds up.
It depends on your dispute policy and whether the transaction stayed inside the mandate. In-mandate purchases typically fall to the user, out-of-mandate ones to the platform.
Yes. Provision network tokens scoped per agent rather than sharing user credentials. Scoped tokens allow instant revocation without disrupting the user’s other payment methods.
Card networks are furthest along with trusted agent frameworks. ACH, UPI, and account-to-account rails work technically but rely on your own mandate layer for control.
Run shadow mode against live traffic with no settlement, plus sandbox simulation of edge cases like retries, revocation mid-transaction, and expired mandates before enabling real money movement.